

Add rate limiting - Portal
API Gateway tutorialZuplo PortalStep 2 of 5
Limit requests from each IP address, then test that requests over the limit return a 429 response.
Before you start: Start with a working route from the gateway setup step. Set up a basic gateway
Follow along using
In this guide we'll add simple Rate Limiting to a route. If you don't have one ready, complete Step 1 first.
Rate Limiting is one of our most popular policies - you should never ship an
API without rate limiting because your customers or internal developers will
accidentally DoS your API; usually with a rogue useEffect call in React code.
What's a Policy?
Policies are modules that can intercept and transform an incoming request or outgoing response. Zuplo offers a wide range of policies built-in (including rate limiting) to save you time. You can check out the full list.
Zuplo offers a programmable approach to rate limiting that allows you to vary how rate limiting is applied for each customer, or requests.
In this example, we'll add a simple IP based rate limiter, but you should look into dynamic rate limiting to see the full power of the world's best rate limiter.
-
Add the rate-limiting Policy
Navigate to your route in the Route Designer (Code >
routes.oas.json), click the Policies dropdown, then click Add Policy on the request pipeline.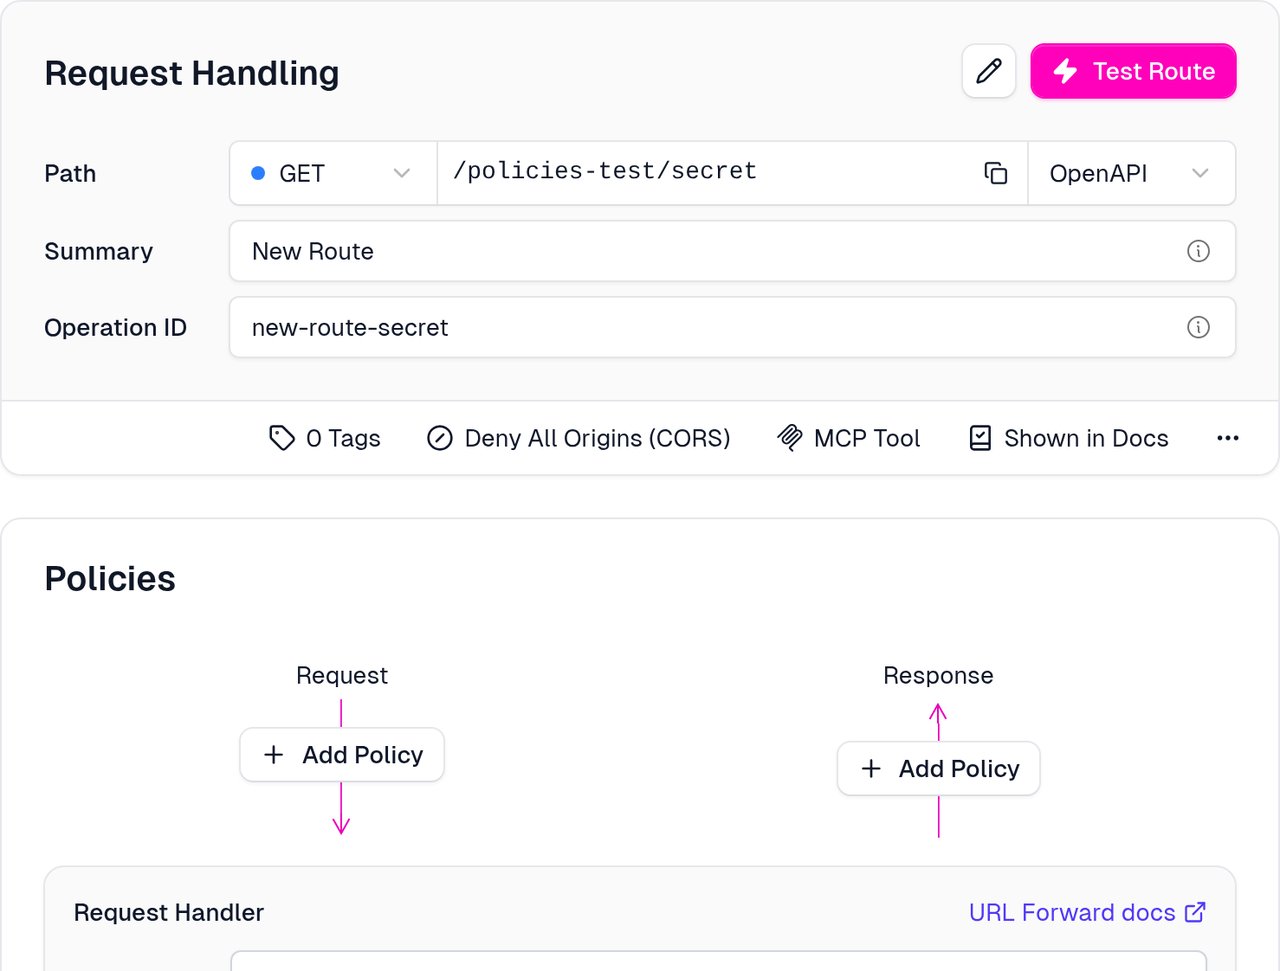
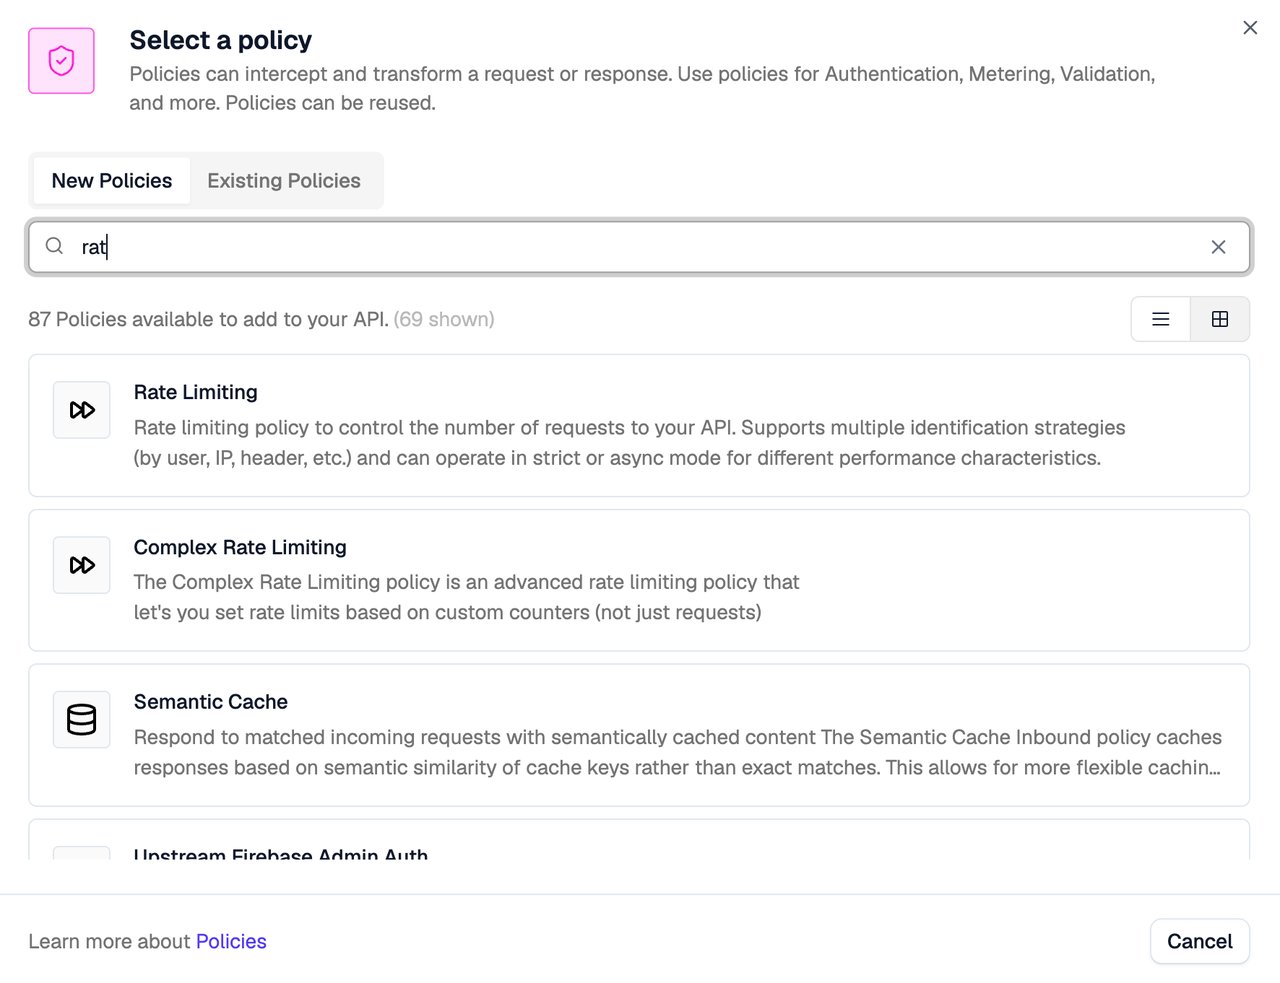
Search for the rate limiting policy (not the "Complex" one) and click it.
By default, the policy will rate limit based on the caller's IP address (as indicated by the
rateLimitByfield). It will allow 2 requests (requestsAllowed) every 1 minute (timeWindowMinutes). You can explore the rest of the policy's documentation and configuration in the right panel.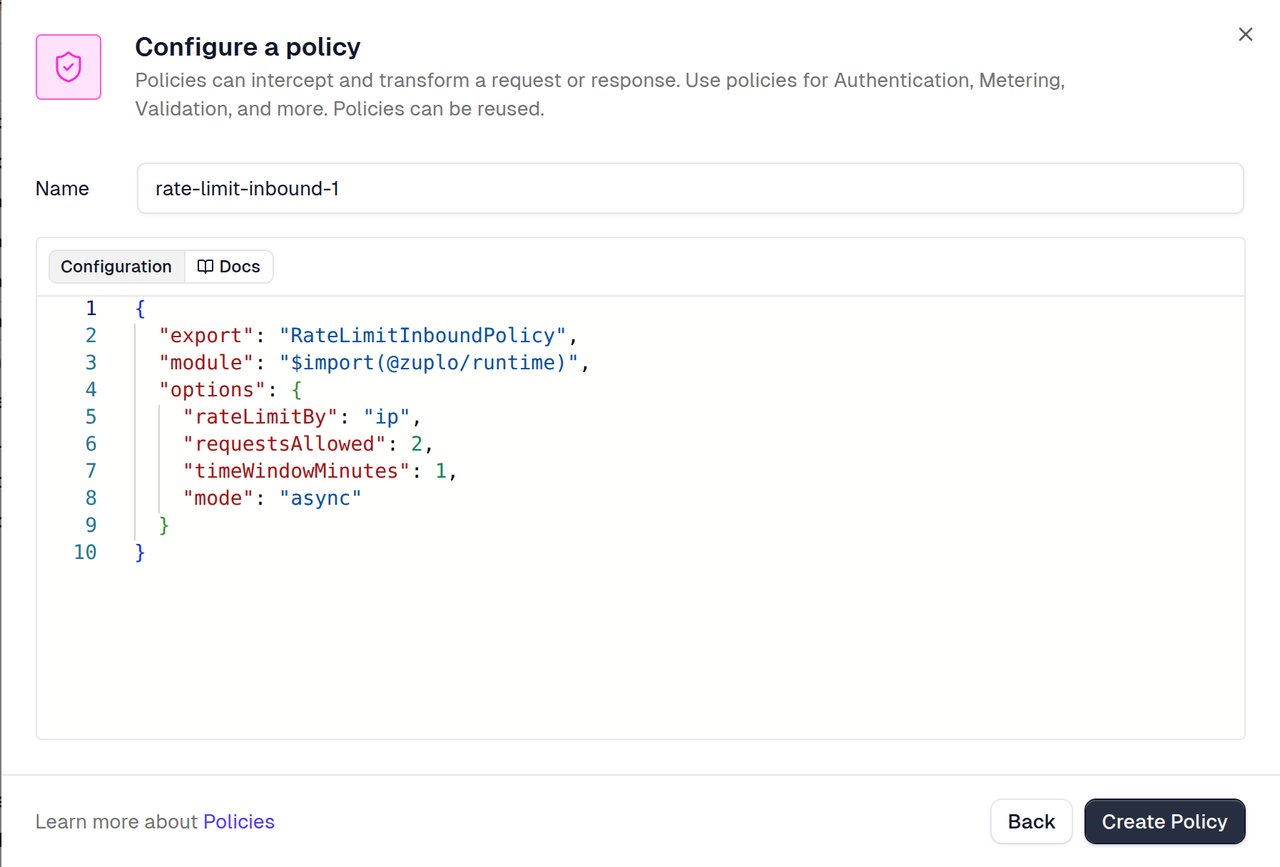
To apply the policy, click OK. Then, save your changes to redeploy.
-
Testing your Policy
Now try firing some requests against your API. You should receive a 429 Too many requests on your 3rd request.
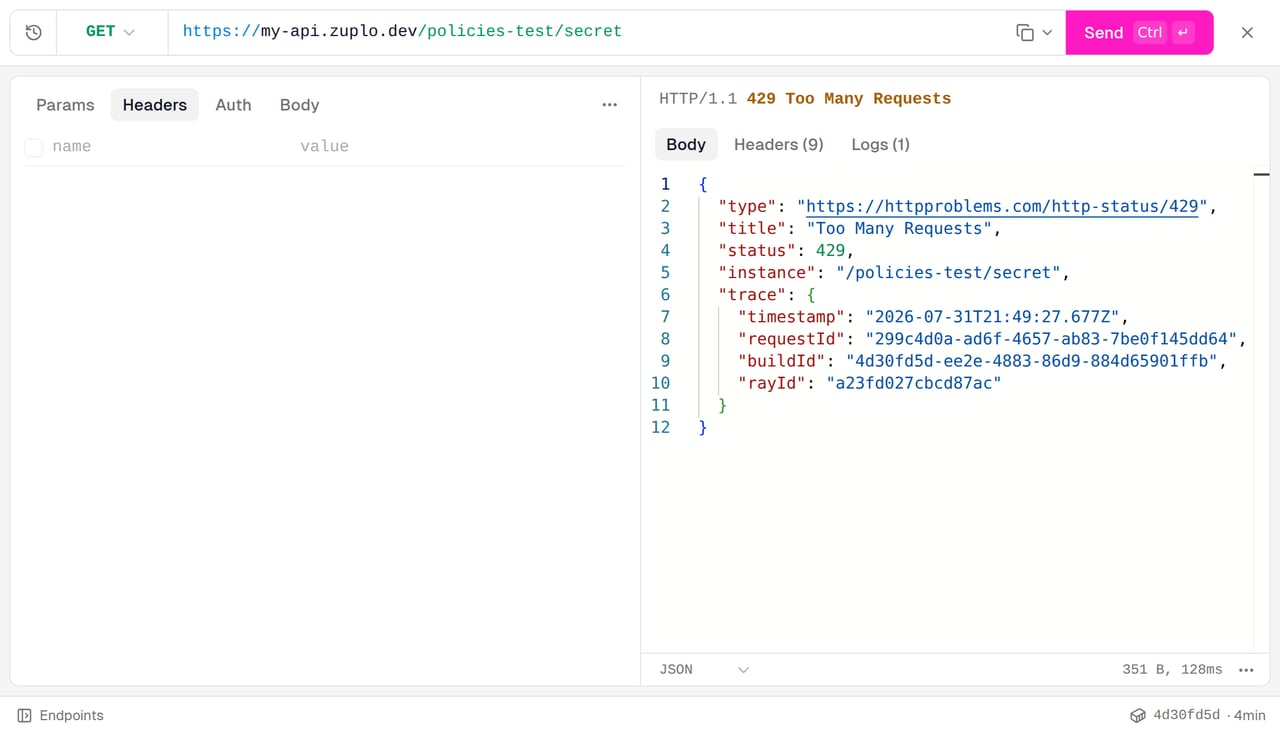
Your rate limiting policy is now intercepting excess requests, protecting the echo API.