

Getting Started with Developer Portal - Editor
Developer Portal tutorialLocal with an editor
Create a developer portal for a sample API, then sign in and test a request with an assigned API key.
Follow along using
Build a developer portal with API reference documentation, a custom introduction, and API key management. You'll run it locally, sign in as an API consumer, and make an authenticated request from the API playground.
Prerequisites
- Node.js 24 or later and Git.
- A Zuplo account.
- An editor and an email address you can use to sign in to the developer portal.
Create and customize the portal
-
Create a project
Run:
CodeWhen prompted, choose Yes to create a matching Portal project, complete sign-in, and select your Zuplo account. The CLI creates a hosted project and links your local copy to it. Keep
.env.zuploout of source control.The default template includes a Todo API and a developer portal. Open the Docs Server URL printed in the terminal, normally http://localhost:9200. You should see the Todo API reference. The gateway runs on port
9000and the Route Designer on9100.Use an existing project
If your project already has a
docsdirectory, clone its Git repository, runnpm installat the project root, then runnpx zuplo loginandnpx zuplo link, selecting the project's working copy. This walkthrough uses the Todo template; for your own API, apply the policy and tests to an equivalent read-only route. Start all three services withnpm run devfrom the project root. For an older project withoutdocs, first follow Enable the Developer Portal. -
Set your portal's title and introduction
Open
docs/zudoku.config.tsx. Setsite.titleandmetadata.titletoTodo Developer Portal, and setmetadata.descriptiontoExplore the Todo API and manage your API keys.Keep the other settings.The
apisentry already reads../config/routes.oas.jsonand publishes it at/api. Your API documentation updates when the OpenAPI file changes.Replace
docs/pages/introduction.mdxwith:docs/pages/introduction.mdxThe default navigation already includes
introduction. Openhttp://localhost:9200/introductionto see the page. Changes appear as you save. See Writing content for more page options. -
Require an API key for the sample route
Replace the empty policy list with:
config/policies.jsonIn
config/routes.oas.json, findpaths["/todos"].get. Update itsx-zuplo-routeto retain the forward handler and add the policy:CodeIf you're using an existing project, add the policy to its existing list and put it first in this route's inbound chain. Leave the other routes and their handlers in place.
anything-goesenables browser requests from the developer portal. For a production API, configure CORS for your portal's origin. This step protectsGET /todos; apply authentication to other routes before exposing private data through them.Update
info.descriptionto say thatGET /todosrequires a bearer API key, replacing the sample's statement that no authentication is required.In a second terminal, run
curl -i http://localhost:9000/todos. Expect401 Unauthorized.
Assign an API key and test it
-
Create a consumer in the Portal
Open your project in the Zuplo Portal and go to Services → API Keys → Consumers. Select Dev, then click Create Consumer.
Set Subject to
tutorial-consumer, add your email address under Key managers, and leave Metadata as{}. Click Save consumer.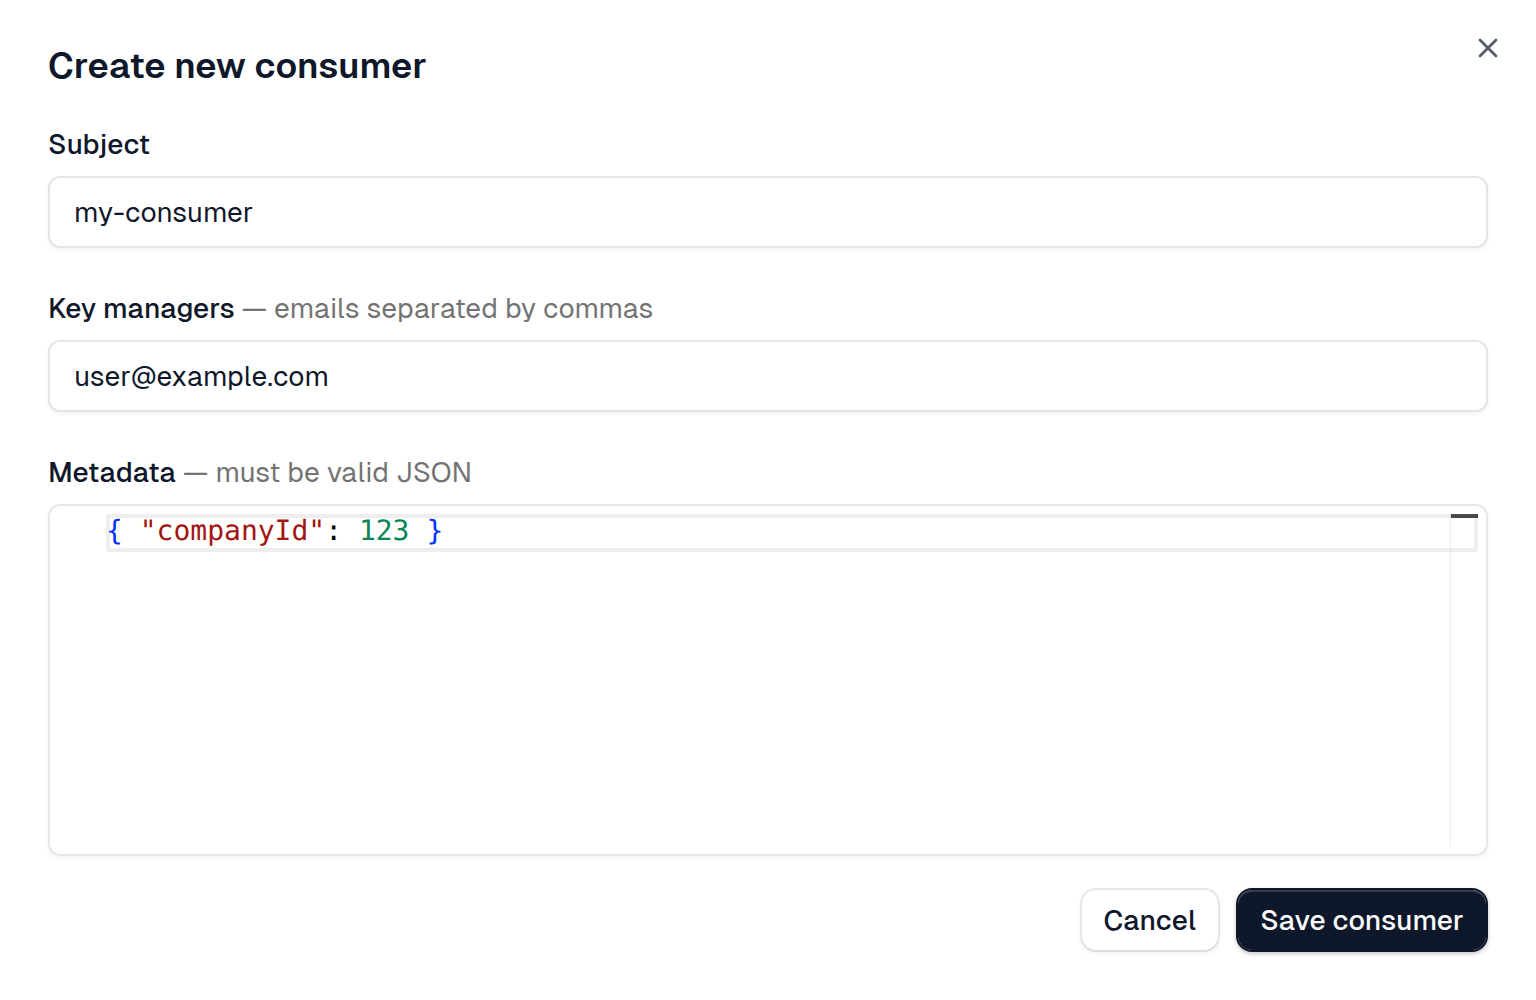
Key managers can view and manage this consumer's keys after signing in to the developer portal. Signing in alone doesn't create a consumer. See API key management.
-
Sign in to the developer portal
Open
http://localhost:9200and sign in with the same email address you entered as a key manager. The template includes a demo sign-in provider andapiKeys: { enabled: true }for this test.Open your profile menu and select API Keys. The assigned consumer and its key should appear. If they don't, check the email address and that you created the consumer in Dev for the linked project.
-
Call the API from the documentation
Open API Reference, select Get all todos, and click Test. Expand Authentication, select
tutorial-consumer, and click Send. Expect200 OKand a JSON response containing todos.You can also copy the key and verify it from a second terminal:
CodeThis request should return
200; the same request without the header should still return401.
Publish the portal
Follow Deploy to the edge to connect your repository and deploy. In the Zuplo Portal, open Deployment URLs and copy the Dev Portal URL. The portal deploys with the gateway.
Create a consumer in the deployed environment's Prod API key bucket and repeat the sign-in and API request there. Development keys are separate from production keys.
Before inviting users or configuring a custom domain, replace the template's demo sign-in configuration with your own authentication provider.
Next steps
- Customize the theme.
- Create consumers on login if every user should receive a key automatically.
- Add more documentation.