Archiving requests to storage
- Applies to
- Gatewayruntime for API, AI, and MCP gateways
- Hosting
- Managed EdgeManaged DedicatedDiffersSelf-HostedDiffers
2 differences by hosting option
Your instance can send outbound traffic from fixed IP addresses, so restricting the SAS token by IP can work. Contact your account team for your instance's addresses.
Outbound requests come from your own cluster's network, so you can restrict the SAS token to your cluster's egress IP addresses.
Note - this sample uses Policies, read this guide first.
In this sample, we'll show how you can archive the text body of incoming requests to Azure Blob Storage. We also have a post on Archiving to AWS S3 Storage.
First, let's set up Azure. You'll need a container in Azure storage (docs). Once you have your container you'll need the URL - click the Properties tab of your container as shown below.
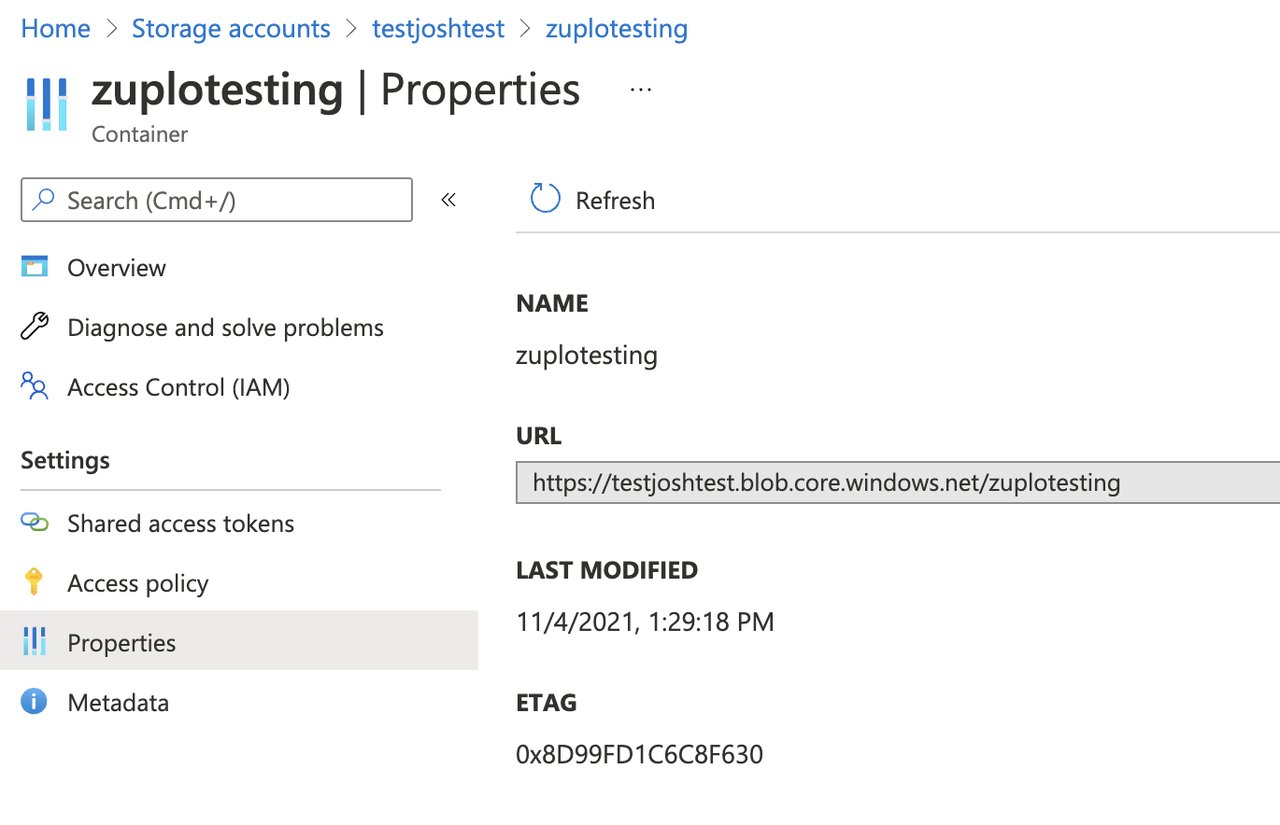
This URL will be the blobPath in our policy options.
Next, we'll need a SAS (Shared Access Secret) to authenticate with Azure. You
can generate one of these on the Shared access tokens tab.
Note, you should minimize the permissions - and select only the Create
permission. Choose a sensible start and expiration time for your token. Note, we
don't recommend restricting IP addresses because Zuplo runs at the edge in over
300 data centers worldwide.
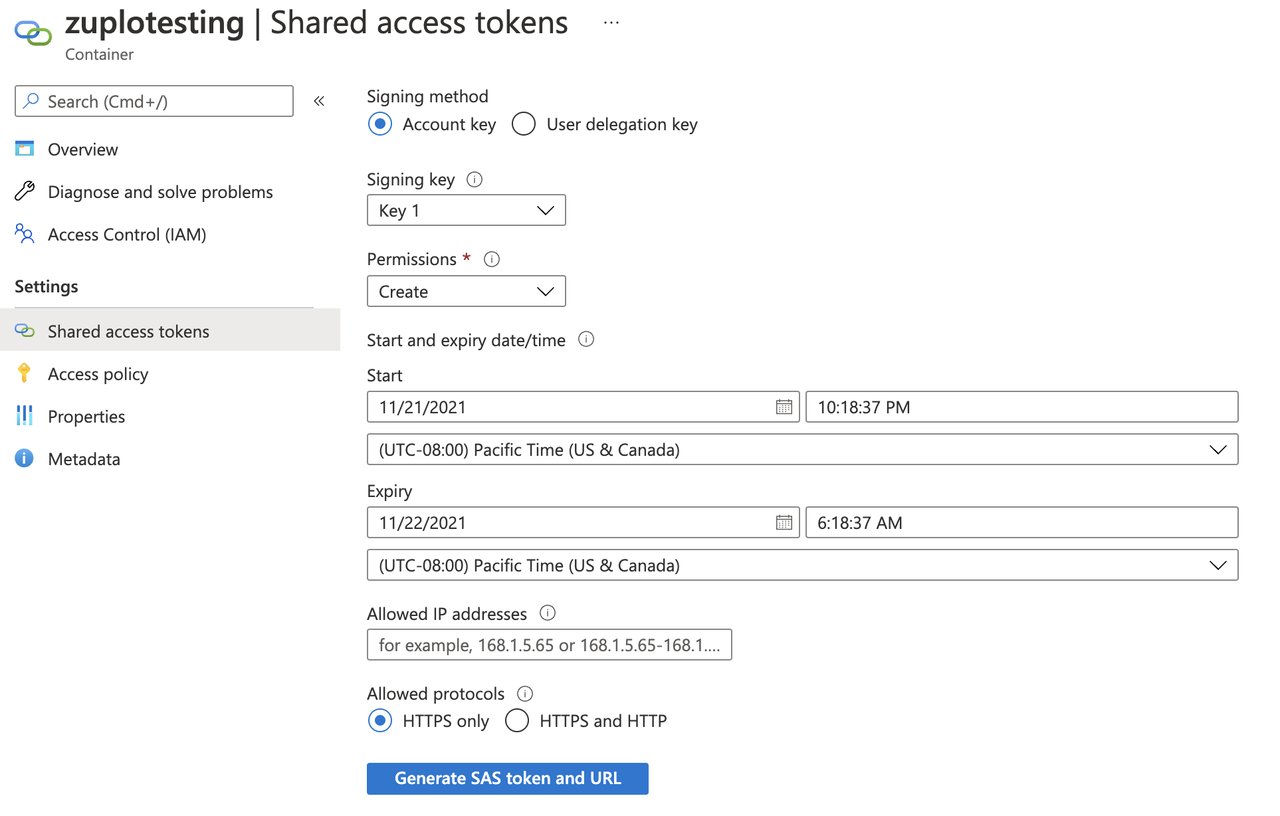
Then generate your SAS token - copy the token (not the URL) to the clipboard and
enter it into a new environment variable in your API called BLOB_CREATE_SAS.
You'll need another environment variable called BLOB_CONTAINER_PATH.
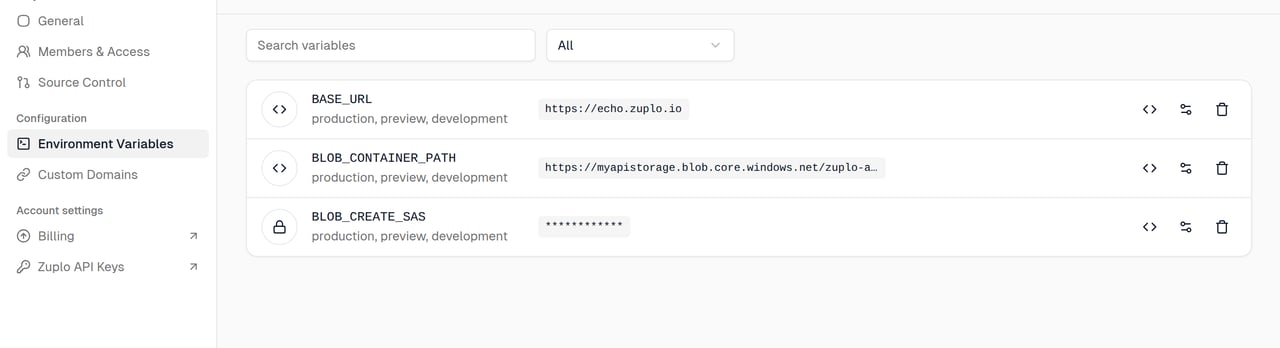
Note - production customers should talk to a Zuplo representative to get help managing their secure keys.
We'll write a policy called request-archive-policy that can be used on all
routes.
modules/request-archive-policy.ts
Finally, you need to configure your policies.json file to include the policy, example below:
Code
Don't forget to reference the request-archive-policy in the policies.inbound
property of your routes.
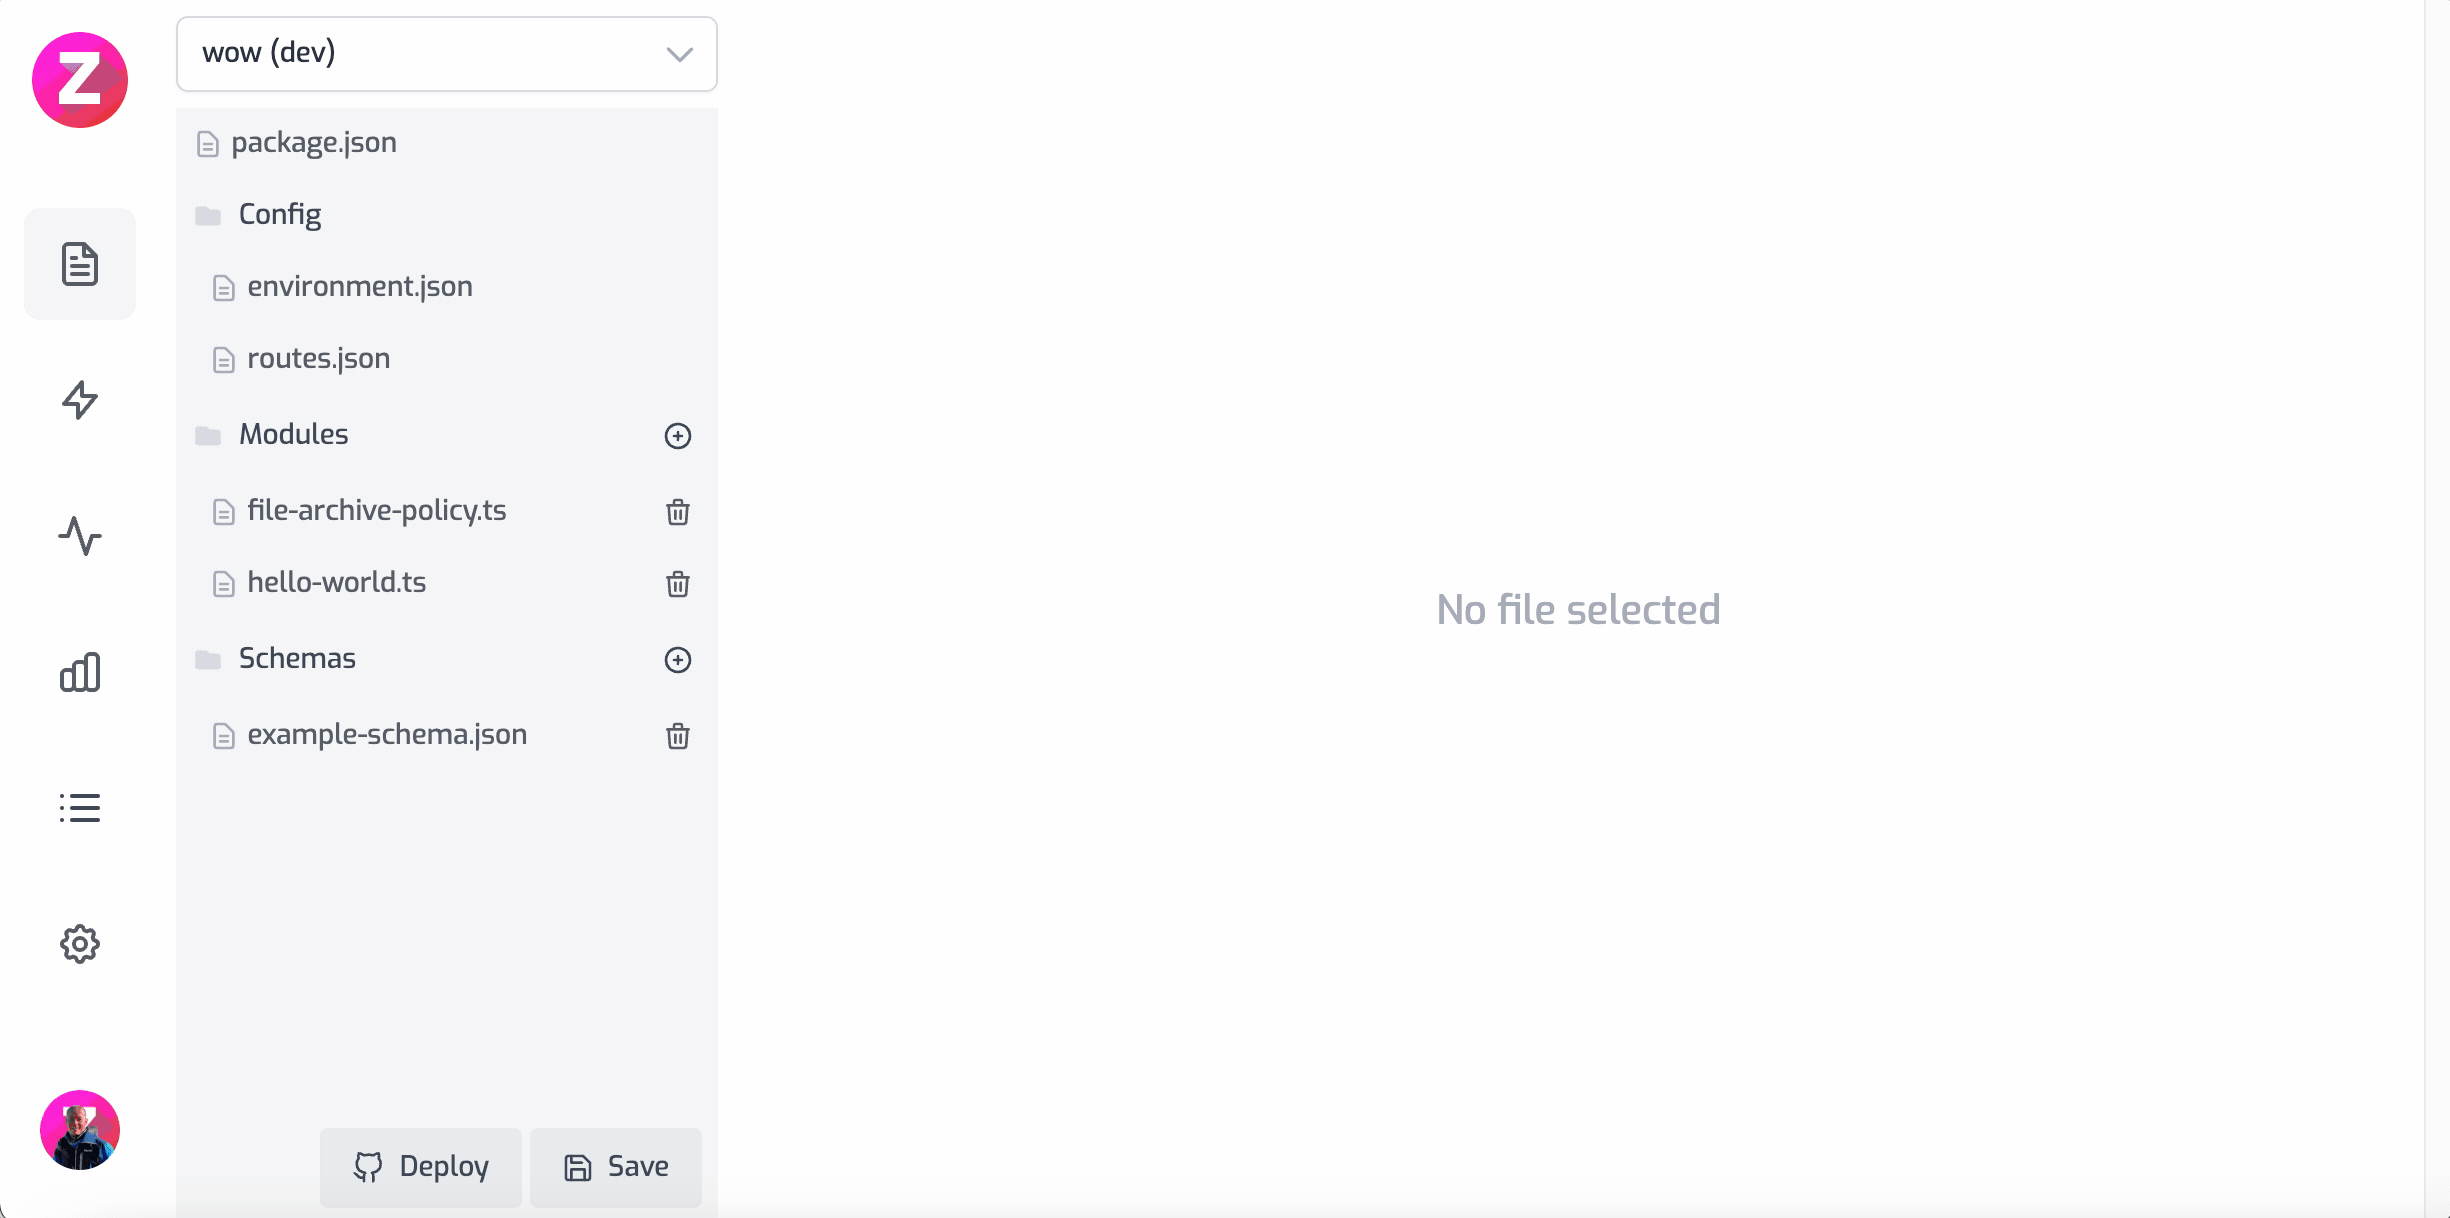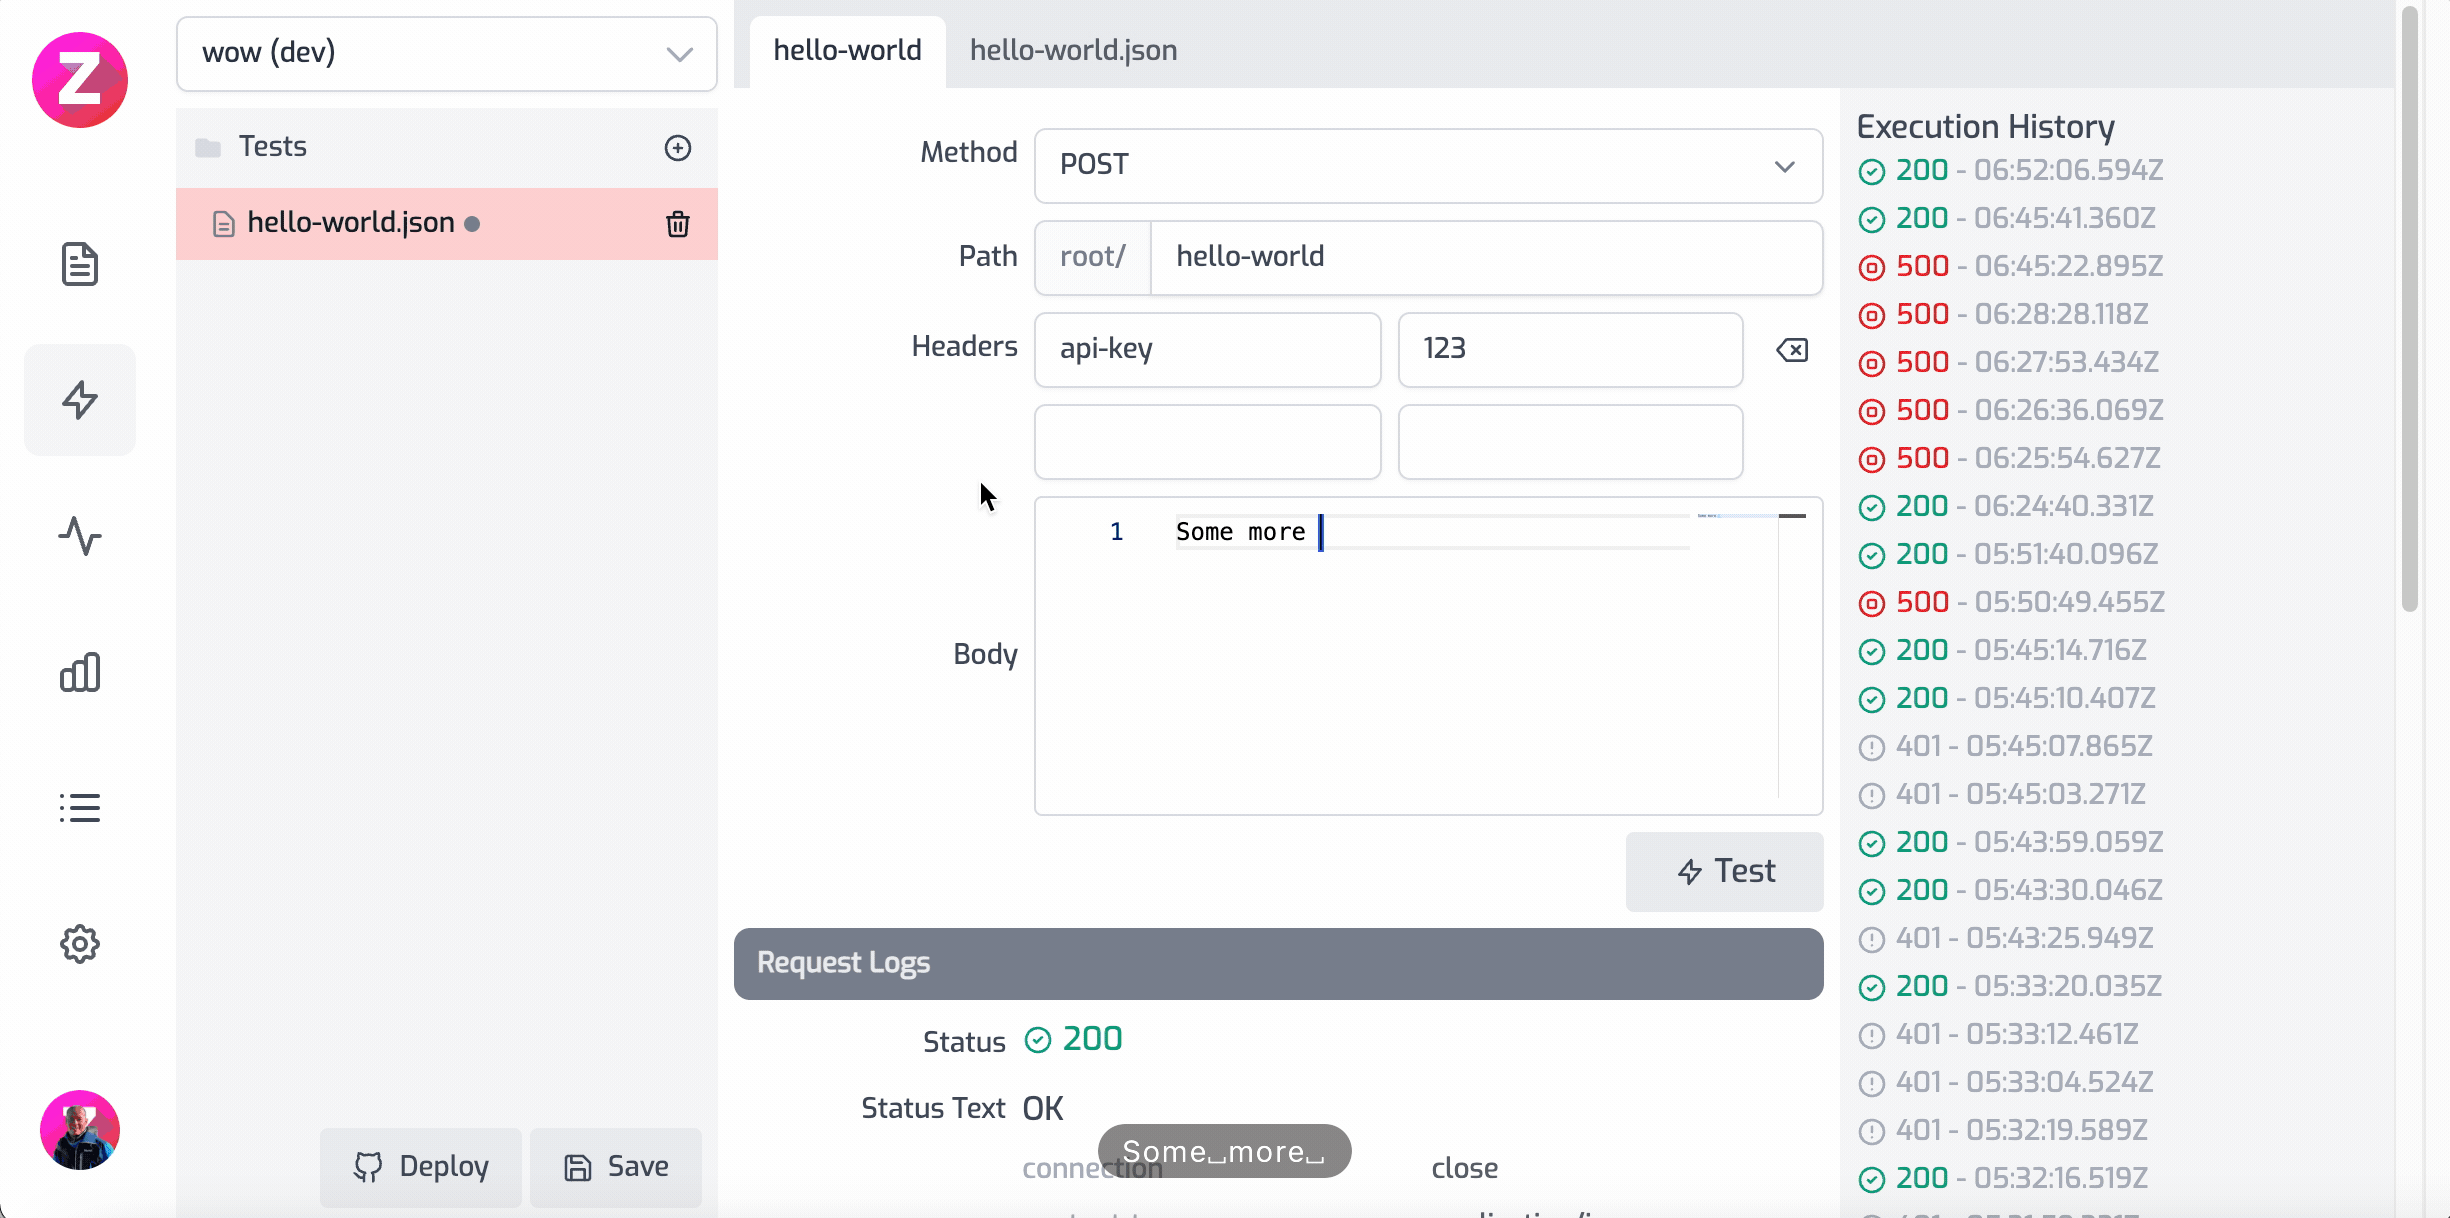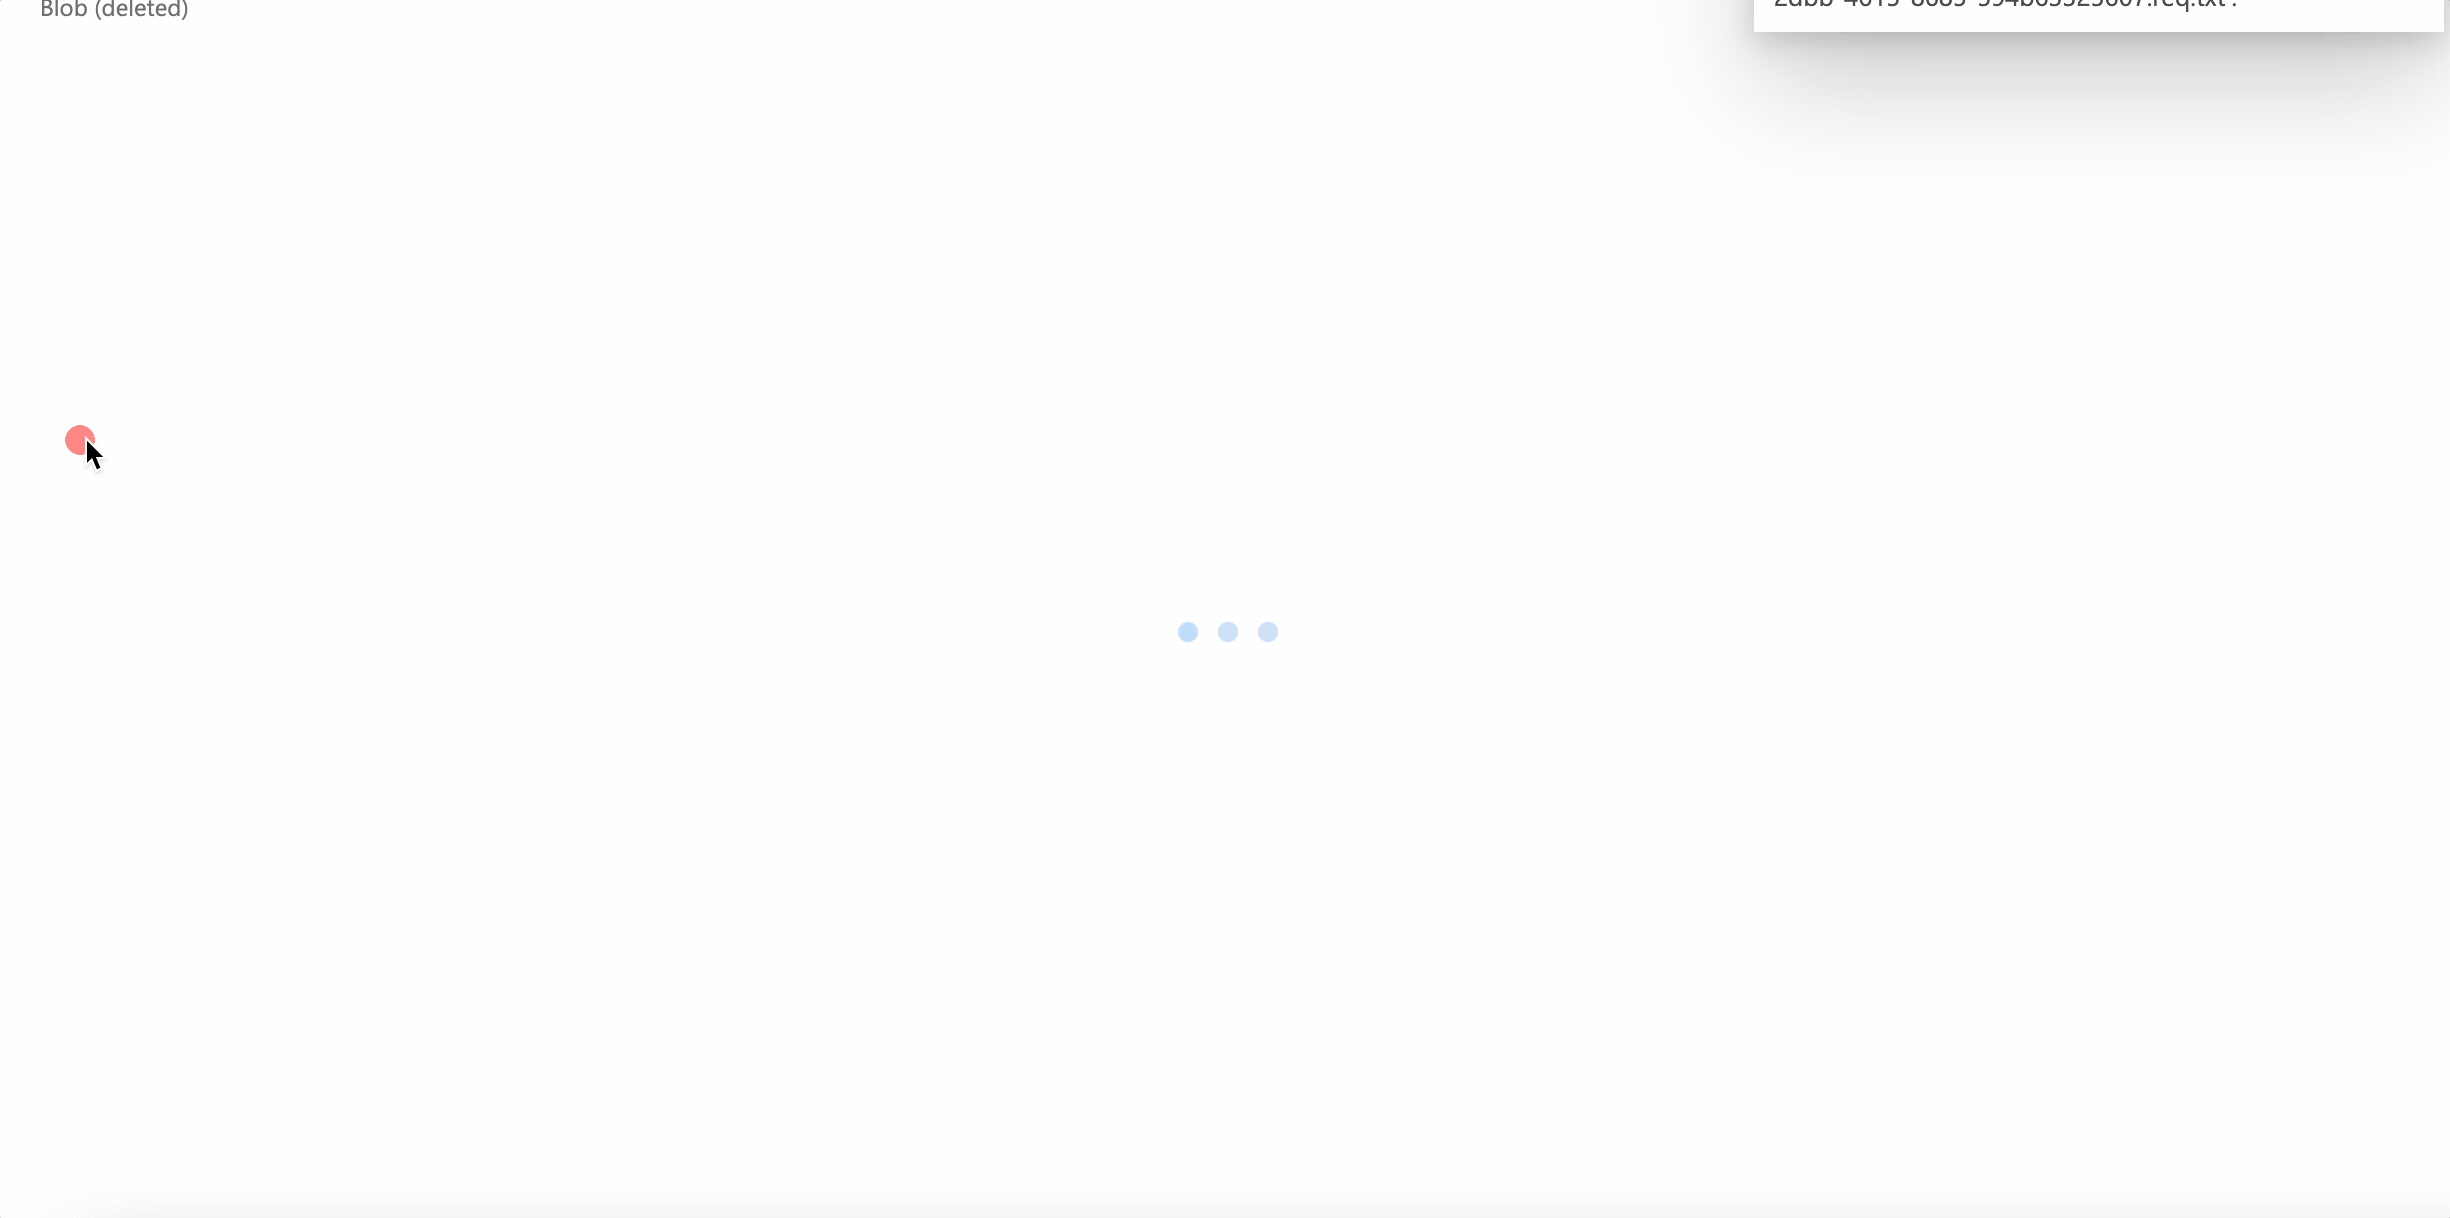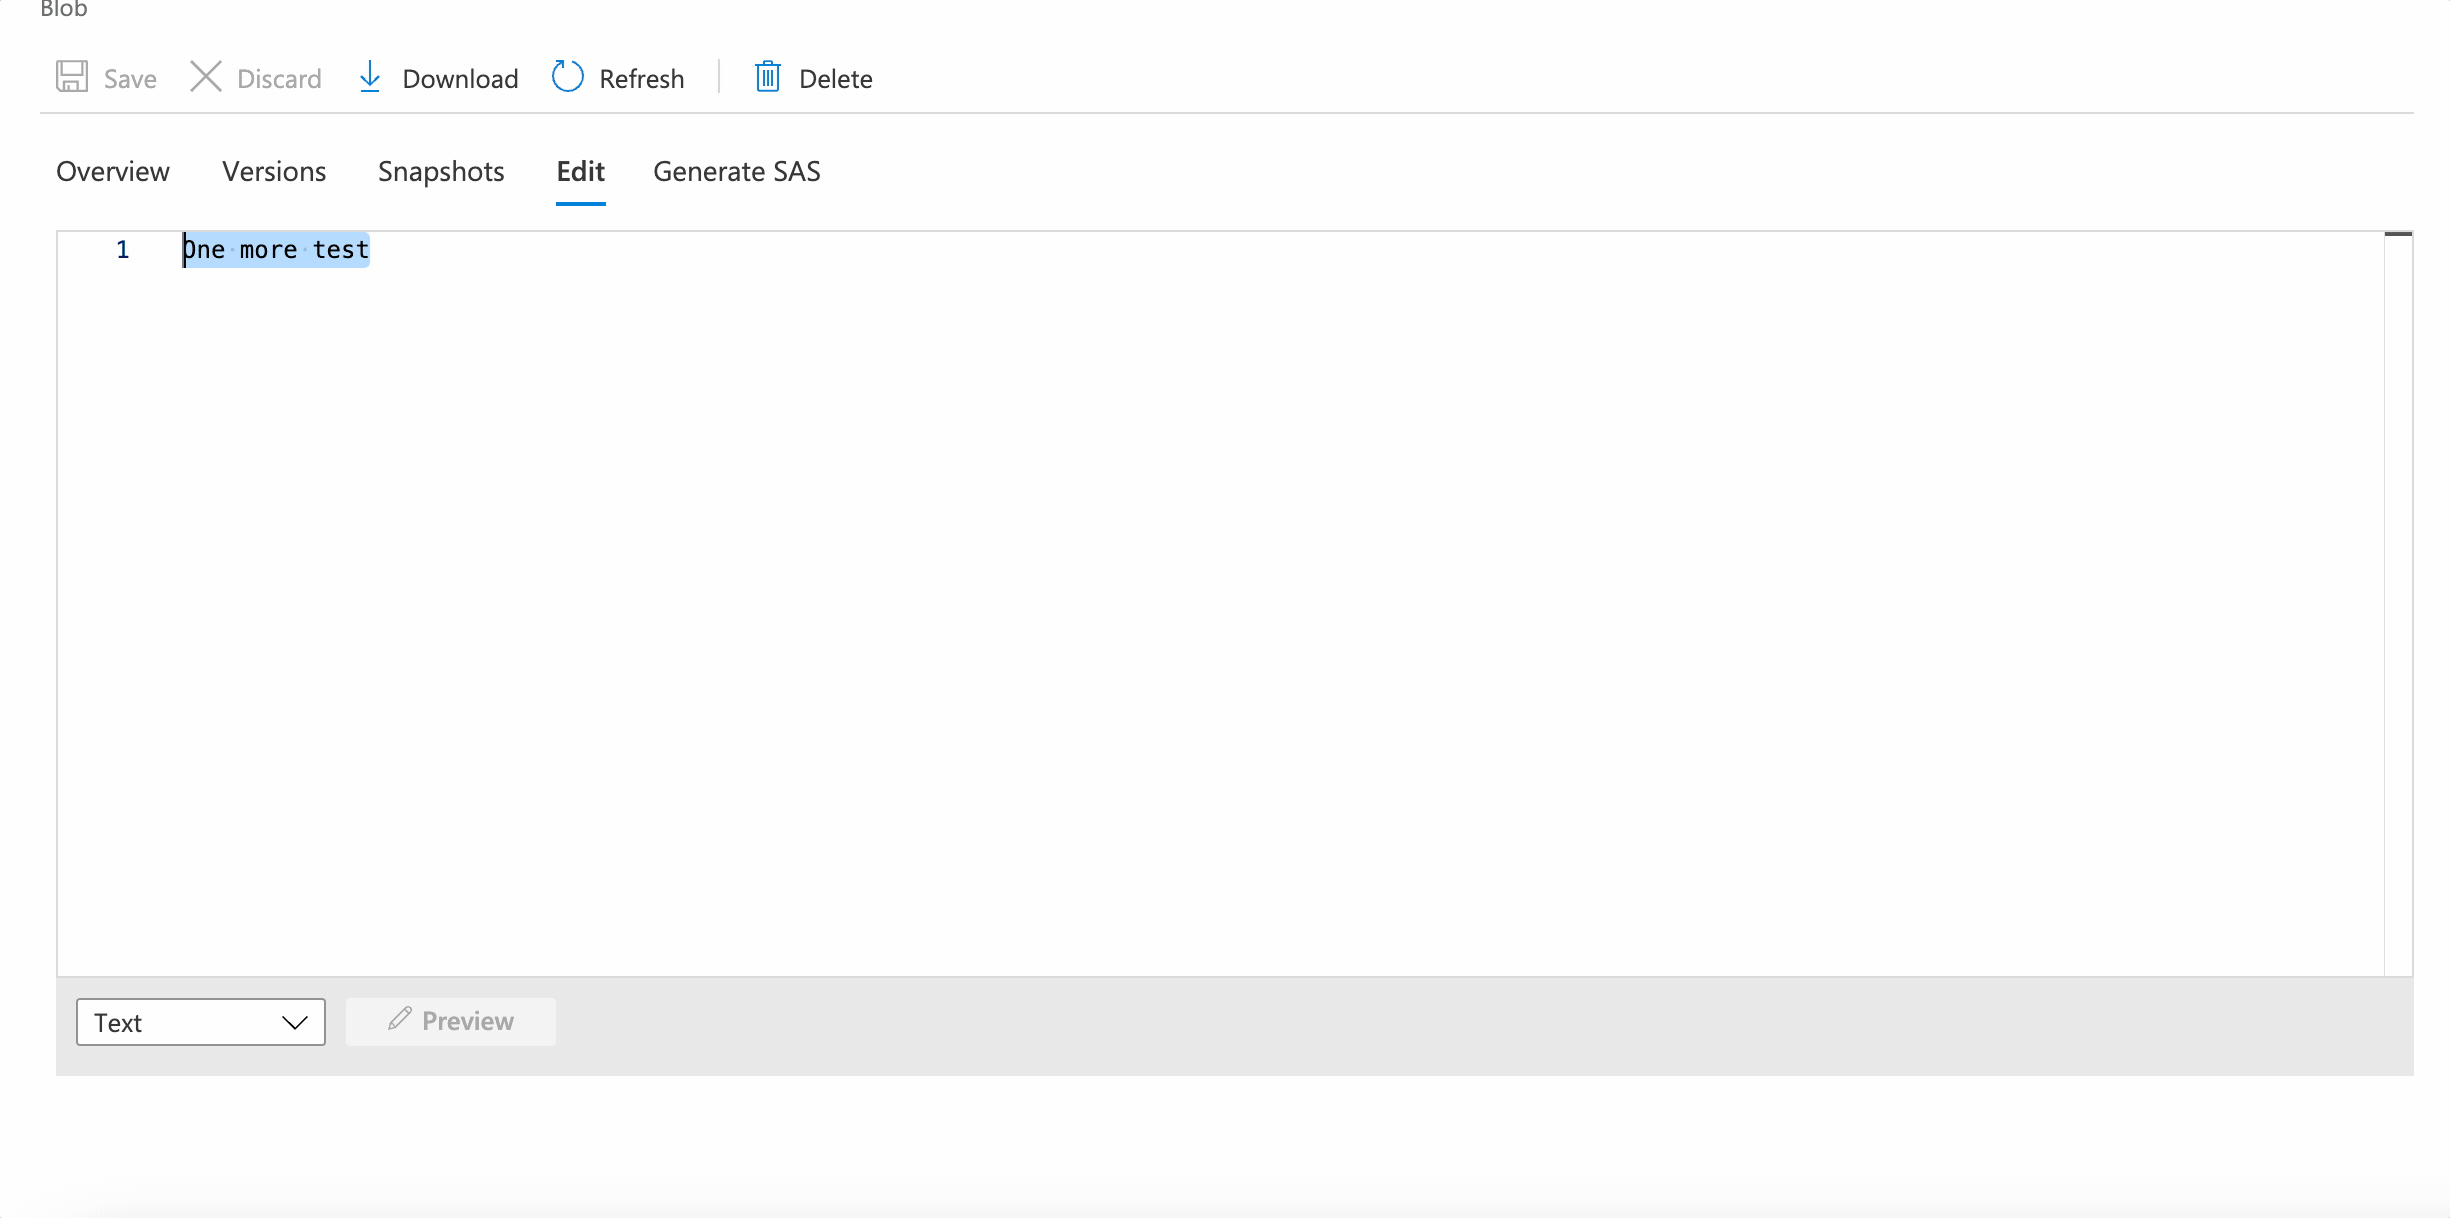
Here's the policy in action: